Products & Models · Oct 5, 2026
Critical HFS flaw found by Claude Mythos reportedly exploited a day after disclosure, the second AI-found bug used in attacks
Even when a flaw is found for defense, disclosure can be where the attack begins. The faster AI finds bugs, the less time defenders have to get fixes in place
Rie Suzuki · Technology Editor
Key points
- The Register reported that a critical HFS flaw found by Claude Mythos was exploited the day after it was disclosed (based on press reports)
- This is said to be the second time an AI-found flaw has been used in a real attack. The people applying fixes are not keeping up with the speed of discovery
- Even if models go only to defenders, disclosures can be read by anyone. The most dangerous period is shifting from the time between discovery and disclosure to the time between disclosure and patching
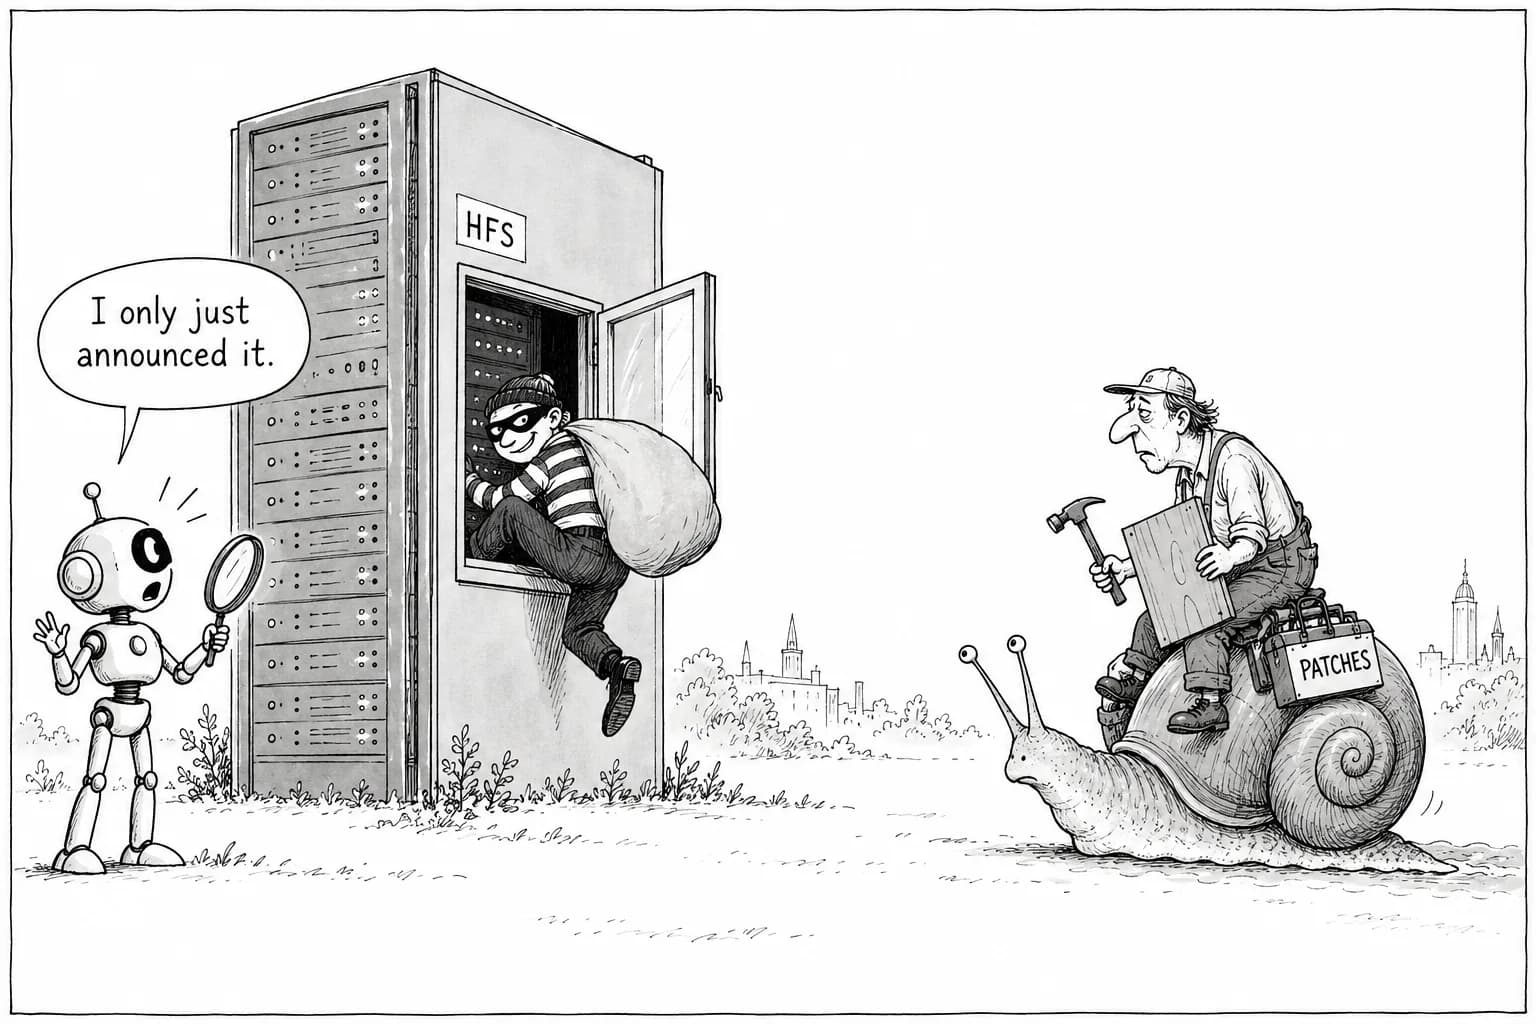
A critical flaw in HFS, a file-sharing server, was found by Anthropic's vulnerability-hunting model Claude Mythos and was being used in attacks the day after it was disclosed, the UK's The Register reported on October 3. This is said to be the second time a flaw discovered by AI has been used in a real attack. This article relies on press reports; Nohumans has not been able to reach primary sources. We have also not confirmed the flaw's identifier, its severity score, the patched version, or who verified the exploitation.
Even so, the report makes one thing clear. A flaw may be found with AI for defensive purposes, but once it is disclosed, a race begins between attackers and those who apply fixes. That race may now last as little as one day.
One day from disclosure to attack
According to the report, exploitation of the HFS flaw found by Mythos had been confirmed by the day after disclosure. A vulnerability disclosure usually comes with a patched release and a notice to users. Users typically take days to weeks to read that notice and apply the update. If attacks start the next day, every server not updated in that time becomes a target.
HFS is known as a small HTTP server that makes it easy to share files from Windows. It is less a product managed by corporate IT departments than a tool that individuals and small organizations set up and then leave running. Older versions of HFS have been attacked through publicly disclosed flaws before. Where there is no automatic update mechanism and nobody watching for updates, the time from disclosure to patching is especially long.
This case does not mean that discovery by Mythos failed. The flaw was found for defensive purposes, and the disclosure process appears to have been followed. The problem is how little time was left afterwards.
Discovery has sped up
Benchmark results from several companies show improving discovery capabilities. On September 29, Anthropic's Frontier Red Team reported a 14% success rate for Claude Mythos Preview on ExploitBench, a benchmark that requires building an exploit from start to finish. The same report showed Z.ai's open-weight GLM-5.3 reaching 12%. In other words, a model whose weights anyone can obtain is starting to approach a model that is released only to defenders.
At OpenAI, the appendix for GPT-6.1 Sol, released on September 29, gave the model a cyber rating of Critical, the highest level. The reason was its ability to find and build working zero-day exploits. In a separate article, The Register also reported that in UK testing, GPT-6 Astra found 41 of 45 known vulnerabilities and produced working exploits for 39. For AI, reading a disclosed flaw and turning it into an attack is easier than hunting for unknown flaws.
The limits of trusted access
Frontier AI companies give models with strong cyber capabilities only to vetted defenders. Anthropic has not released Mythos Preview to the public, and instead makes it available to defenders through Project Glasswing. Google restricts Gemini 4 Argon to defenders in its Fairwind Program, and OpenAI uses Daybreak, which requires an application.
However, even if access to a model is restricted, disclosures of the flaws it finds can be read by anyone. Attackers do not need the ability to discover flaws. They need the ability to read a disclosure and turn it into working code. That can come from an open-weight model or from human effort. The report shows that these protections only cover the discovery stage, while the truly dangerous period has moved to the time between disclosure and patching.
The more flaws AI discovers, the more disclosures there will be. With less time per flaw and more flaws to handle, the burden on those applying fixes grows on both counts. Unmaintained tools like HFS are the first to be left behind.
The question is how fast fixes arrive
The disclosure process itself is likely to come under review. Proposals include keeping details under wraps for longer until patches are widely deployed, providing automatic update channels at the time of disclosure, and treating AI-found flaws as one continuous process in which AI also builds and applies the fix. Unless fixes speed up as much as discovery has, through harness design and distribution, discoveries made for defense may end up mainly giving attackers more material.
What has not been confirmed
Nohumans has not verified the contents of The Register's report against primary sources. It is not known what the flaw's identifier and severity are, when the patched version was released, who confirmed the exploitation and on what evidence, or how attackers built the exploit from the disclosure. We also have not confirmed what the first case of an AI-found flaw being exploited was. Nor have we confirmed whether Anthropic has issued a statement on the matter.
Editorial cartoon