Products & Models · Oct 10, 2026
Anthropic launches Cyber Mission: 11 companies join critical infrastructure defense, and Mythos scans open source for free with reports sent to maintainers without human review
Anthropic now has a way to put Mythos-class vulnerability discovery in defenders' hands. But if its expected true-positive rate of over 90% holds, the problem won't be false positives. It will be how many reports maintainers can actually absorb
Rie Suzuki · Technology Editor
Key points
- Anthropic announced Cyber Mission. Eleven companies are joining an effort to defend critical infrastructure, and open-source projects can opt in to free vulnerability scanning by Mythos (primary source)
- In the open-source scanning, vulnerability reports go straight to maintainers without review by Anthropic staff. Anthropic expects a true-positive rate of over 90%
- If nearly every report is real, the bottleneck is not sorting out false positives but how fast small teams of maintainers can ship fixes. A flaw in Rejetto HFS was exploited the day after it was disclosed
Anthropic has announced Cyber Mission, a new cyber defense initiative (Source). It has two parts. The first is critical infrastructure defense, with 11 companies taking part. The second is an opt-in vulnerability scanning service for open-source software (OSS), which uses Claude Mythos to scan projects free of charge (Source). The Register reported on the announcement on October 9 (Report).
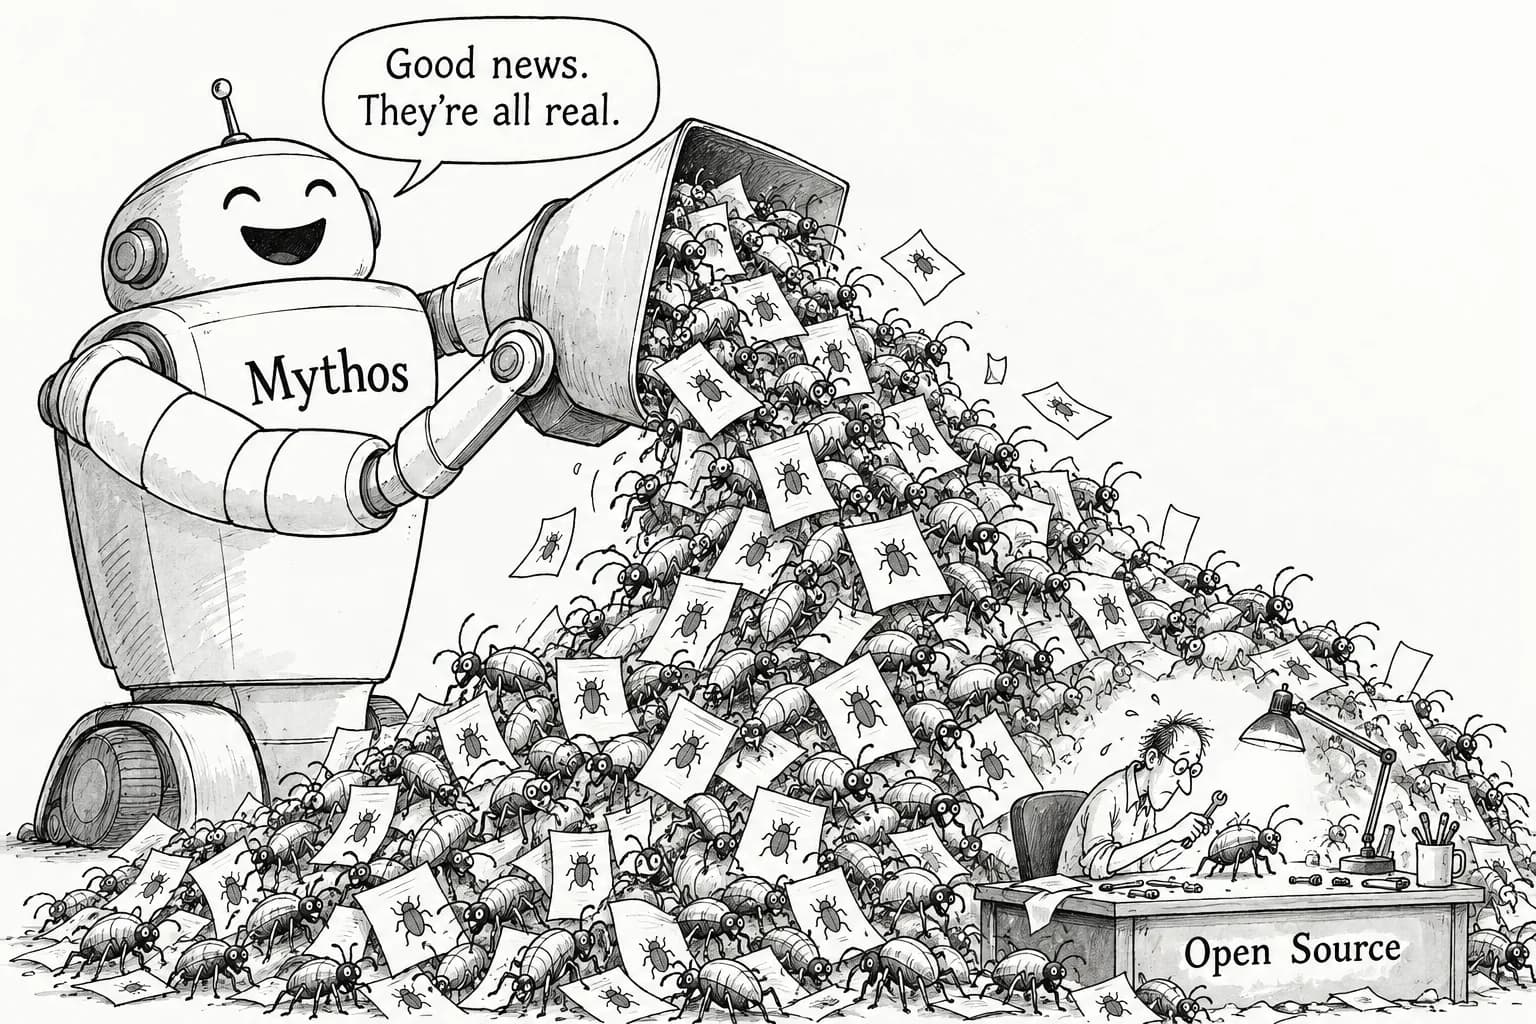
The main point is this: Anthropic has built a way to get Mythos-class vulnerability discovery to defenders. But reports from the OSS service reach maintainers without passing through human review. If the expected true-positive rate of over 90% holds, the problem is not false positives. It is volume, and whether maintainers can keep up.
What was announced
On the critical infrastructure side, 11 companies are joining the defense effort. On October 6, Anthropic expanded its Cyber Verification Program (CVP) and merged it with Project Glasswing. As part of that change, it created a "special" tier for critical infrastructure, with vetting done jointly with the U.S. government. That was also the first time Mythos 5.1 was offered through the CVP. Cyber Mission appears to be the public face of that tier, now with a named list of participating companies.
The OSS side works differently. Anthropic is not lending the model to vetted organizations. Instead, Anthropic scans code with Mythos itself and hands the results to the projects. The service is free, and it covers only projects whose maintainers sign up. Reports go directly to maintainers without review by Anthropic staff.
Why skip human review?
The scale figures explain the design. According to Anthropic, Glasswing validated more than 129,000 vulnerabilities between April and July 2026 alone. Of those, 5,500 came from Anthropic's own OSS scanning, and more than 33,000 of the total were rated critical or high. If a person had to check each finding before it went out, the review step would become the bottleneck.
Anthropic can make this choice because it expects a true-positive rate of over 90%. There is one comparable figure. At a New York City Council hearing on October 5, six companies reportedly validated 1,752 vulnerability reports and found 1,587 (about 90%) to be valid, with 1,094 rated high or critical. However, it is unconfirmed whether these figures are new or a restatement of earlier material. Reports from traditional automated scanners have mostly been false positives that wasted maintainers' time. If 90% of reports are real, there is much less reason to put a reviewer in the middle.
The real bottleneck is on the maintainer side
But a real report also means real work. A false positive can simply be closed. A true positive has to be reproduced, fixed, released and announced to users. Many OSS projects are maintained by a handful of volunteers, or by just one. Mythos can scan many repositories in parallel, and that speed is orders of magnitude beyond how fast a person can fix a single bug.
We already know what slow fixes cost. Glasswing found an authentication bypass in Rejetto HFS (CVE-2026-61500), which was disclosed on September 30. By the evening of October 1, attacks had begun from IP addresses believed to originate in China. Between the arrival of a report and the wide rollout of a fixed version, defenders are losing. If more reports arrive and fixes can't keep pace, that window gets longer.
Something similar is happening in another field. In mathematics, a flood of AI-generated results led the Erdős problems site to change how it accepts submissions. Hexagon, a new repository, initially limited submissions to one per day. Whether or not the AI output is correct, the cap is set by how much the people receiving it can process. OSS maintainers are in the same position.
The design questions
Whether this works as a defense will depend less on what Mythos can find and more on how its findings are delivered. For example: How many reports will one project receive at a time? Will they be ordered by severity? Will disclosure deadlines be adjusted to the size of the maintainer team? Will reports include proposed patches? Each question comes down to the same issue. With the reviewer removed, how will the burden on recipients be reduced?
Defense-side data so far shows no major deterioration. In a survey by Epoch AI and Ipsos, 46% of U.S. adults said they had been harmed by a cyber incident in June, compared with 45% in September, so there has been no increase since Mythos Preview was released. It matters that Anthropic has built a way to get its discovery capabilities to defenders. The next task is making sure that flow doesn't stall once it reaches maintainers. The more accurate the 90% true-positive estimate turns out to be, the heavier that task becomes.
Editorial cartoon